Release notes · 8.1.0 development
8.1.0-RC1
The first release candidate of the 8.1.0 line turns Palantir into a place to manage authorization policies, attribute repositories and cluster topology, and lets OAuth and OpenID Connect applications rotate multiple client secrets.
- Requires JDK 25
- Built on Spring Boot 4.2
- Built with Gradle 9.7
- 556 browser test scenarios
- 15New & noteworthy topics
- 5Changes to review before upgrading
- 13Other changes
- 0Fixes
Before You Upgrade
These changes alter existing behavior. Each one links to its full description below.
-
Action
Palantir admin functions now require a released
roleattribute ofADMINorROLE_ADMIN; other users only manage registered applications.Platform & Operations - Changed
-
Changed
Date formatting in a number of operations now uses
UTCinstead of the system default time zone. -
Changed
CAS REST APIs answer unauthorized application requests with
403instead of a500error.CAS & Other Protocols -
Removed
LettuceMod is removed; Lettuce itself now provides its functionality.Tickets & Sessions
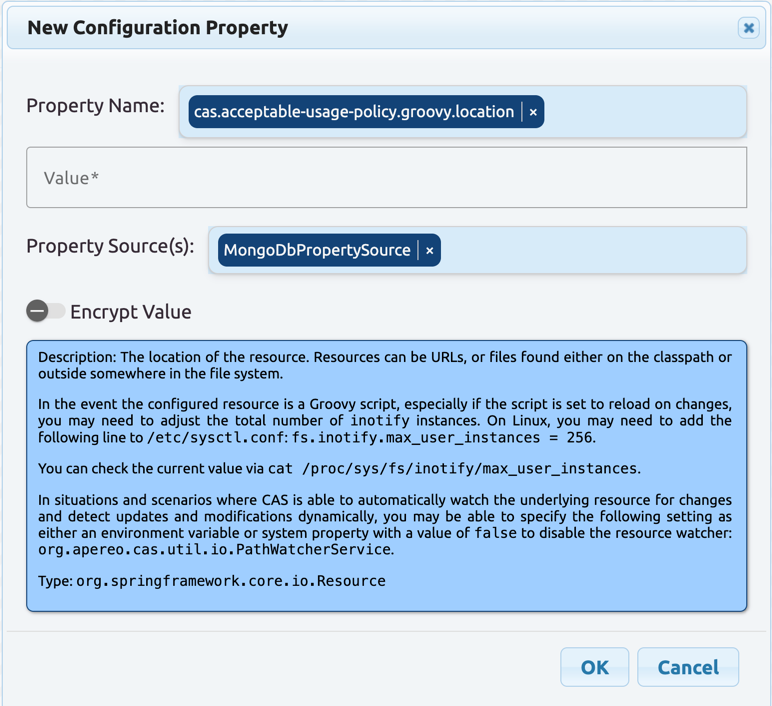
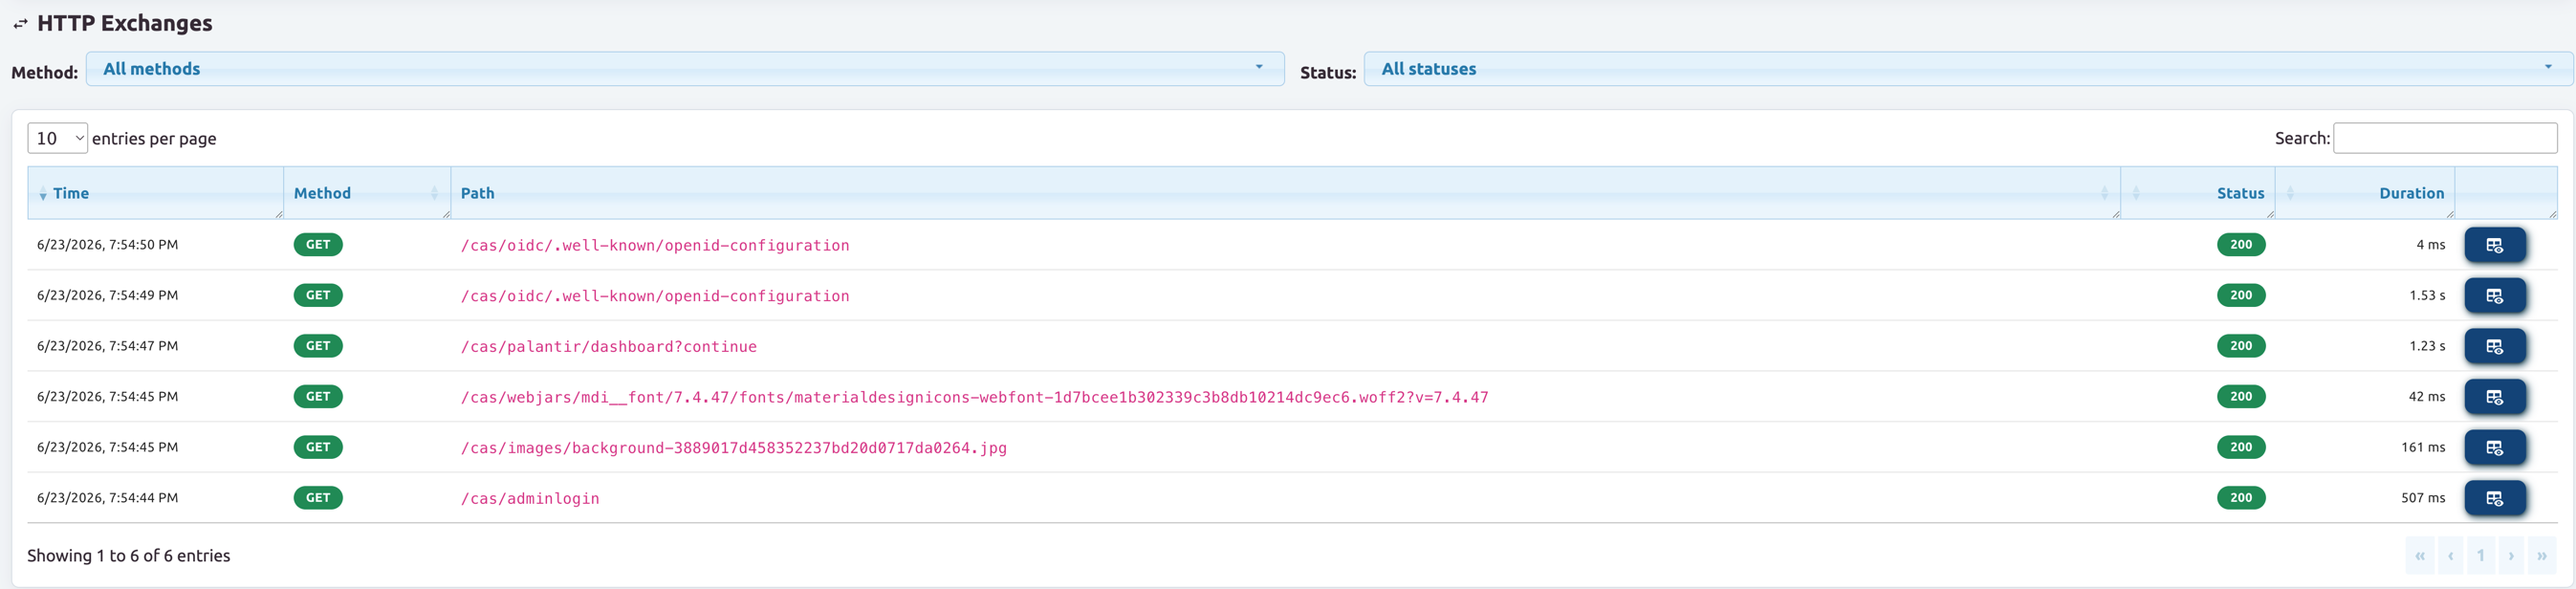
Spotlight · Palantir admin dashboard
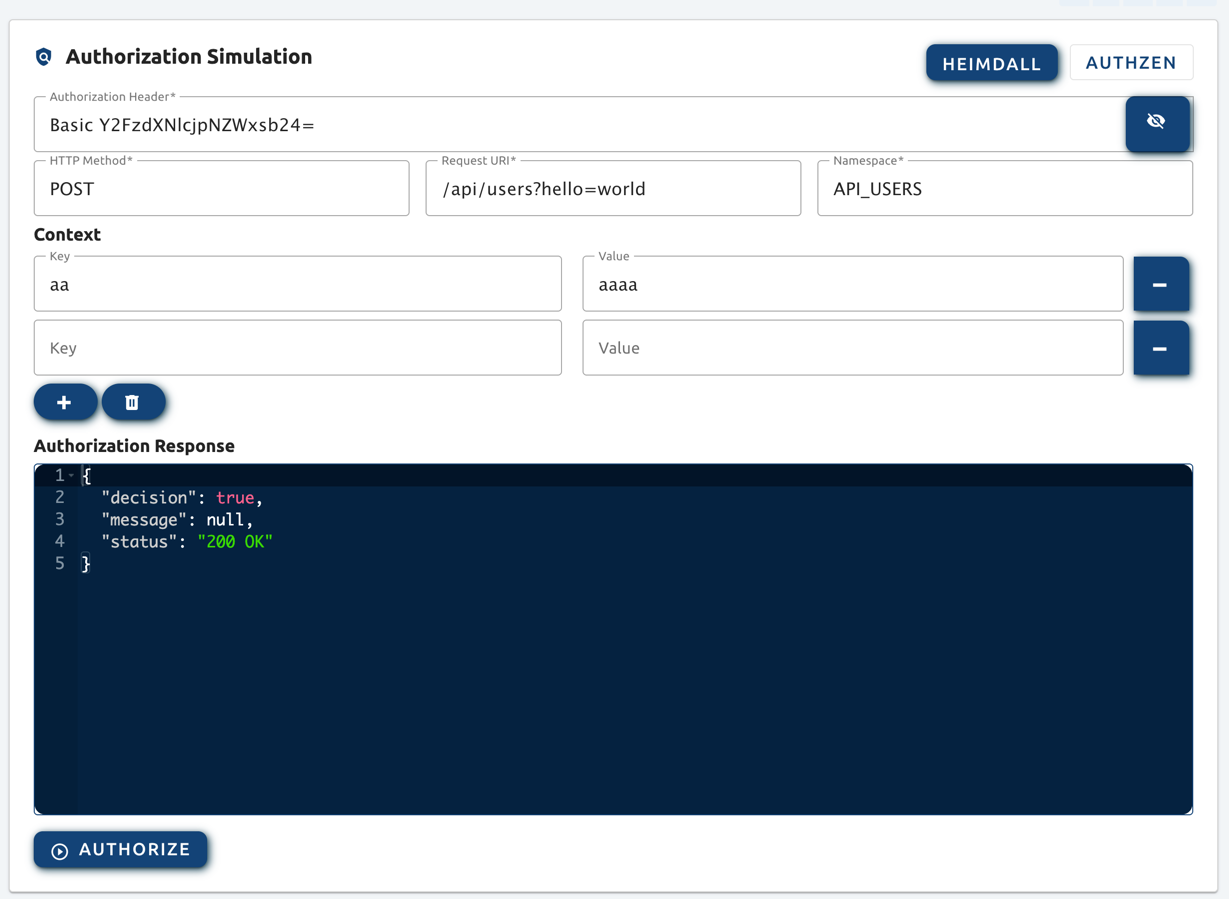
Manage Authorization from the Dashboard
- Create, edit and remove Heimdall authorization policies, and simulate authorization requests.
- Right-click context menus replace inline table buttons.
- View attribute repositories in detail and register LDAP, JDBC and stub repositories.
- Inspect, remove or recompute cached scripted resources, and edit inline Groovy in a dedicated editor.
Highlights
-
OAuth & OpenID ConnectNew
Multiple Client Secrets
Applications can hold several expiring client secrets for smooth rotation, managed through the
oauthClientSecretsendpoint. -
Platform & OperationsNew
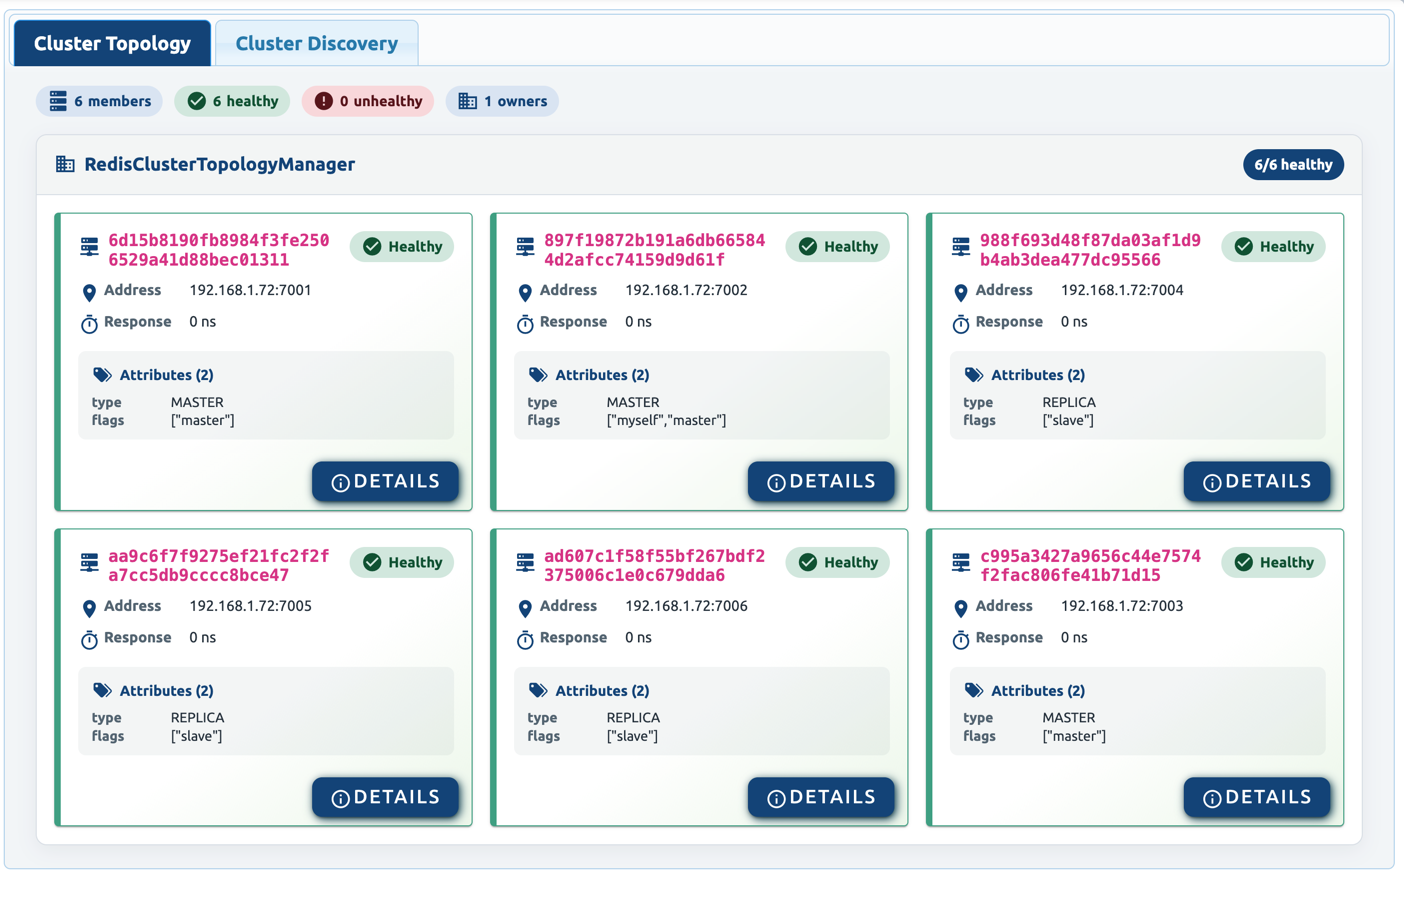
Cluster Topology
A
clusterTopologyactuator endpoint reports every node and its status across eight ticket registries. -
Attributes & ConsentNew
Attribute Definition Dependencies
Attribute definitions can depend on other definitions, which are resolved first and available during resolution.
-
OAuth & OpenID ConnectNew
OpenID Connect Verifiable Credentials
Credential issuance supports the authorization code flow, more formats and initial OpenID4VP support.
-
OAuth & OpenID ConnectChanged
OpenID Connect Federation
Federation support is roughly finalized, with remaining edge cases tracked for the next releases.
-
Interface & AccountsNew
Acceptable Usage Policy & Multitenancy
Acceptable usage policies work per tenant, starting with MongoDb storage.
New & Noteworthy
The following items are new improvements and enhancements presented in this release.
OpenRewrite Recipes
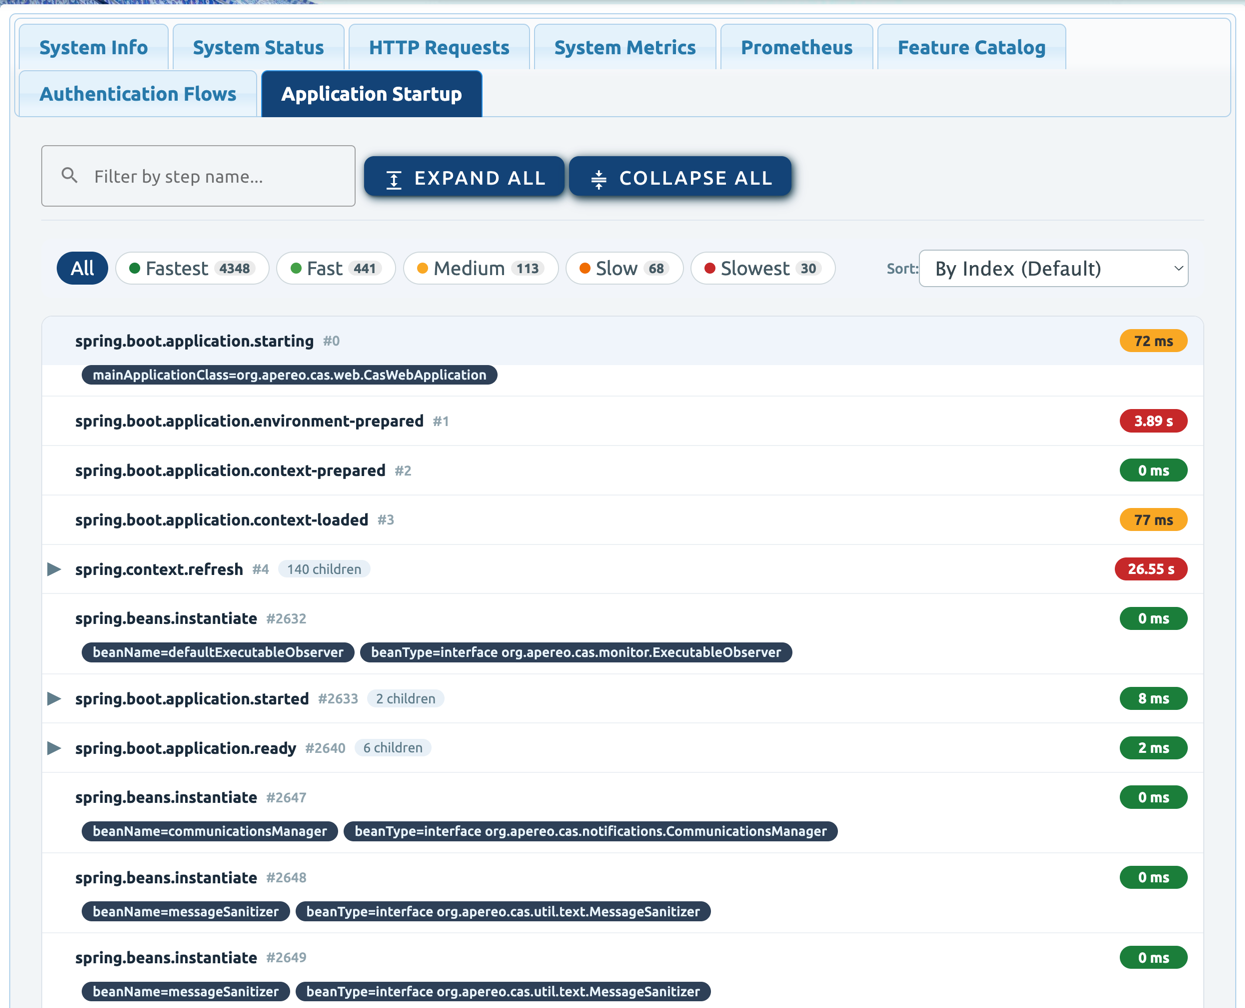
CAS continues to produce and publish OpenRewrite recipes that allow the project to upgrade installations in place from one version to the next. See this guide to learn more.
Graal VM Native Images
A CAS server installation and deployment process can be tuned to build and run as a Graal VM native image. We continue to polish native runtime hints. The collection of end-to-end browser tests based on Puppeteer have selectively switched to build and verify Graal VM native images and we plan to extend the coverage to all such scenarios in the coming releases.
Testing Strategy
The collection of end-to-end browser tests based on Puppeteer continue to grow to cover more use cases
and scenarios. At the moment, total number of jobs stands at approximately 556 distinct scenarios. The overall
test coverage of the CAS codebase is approximately 94%.
Gradle 9.7
CAS is now built with Gradle 9.7 and the build process has been updated to use the latest Gradle features and capabilities.
Spring Boot 4.2
CAS is now built on top of Spring Boot 4.2.x. This is an in-progress ongoing minor platform upgrade that
affects almost all aspects of the codebase including many of the third-party core libraries used by CAS
as well as some CAS functionality.
Please refer to the Spring Boot Wiki for more information on the changes and updates in this release. The biggest change to CAS would be support for AMQP 1.0.
JSpecify & NullAway
CAS codebase is now annotated with JSpecify annotations to indicate nullness contracts on method parameters, return types and fields. We will gradually extend the coverage of such annotations across the entire codebase in future releases and will integrate the Gradle build tool with tools such as NullAway to prevent nullness contract violations during compile time.
OAuth & OpenID Connect Client Secrets
OAuth and OIDC client applications may now define multiple client secrets,
allowing deployments to support secret expiration and smoother secret rotation. Existing
single-secret configurations remain compatible, while new configurations can
include additional secrets with expiration metadata so clients can transition
to new secrets without immediate disruption. Client secret rotation may be carried out using
a dedicated oauthClientSecrets actuator endpoint.
Attribute Definition Dependencies
Attribute definitions may now declare dependencies on other attribute definitions. When an attribute is resolved, its declared dependencies are resolved first and their results are made available during resolution, allowing definitions to build on values produced by other definitions in a predictable, reusable way.
Palantir Admin Dashboard
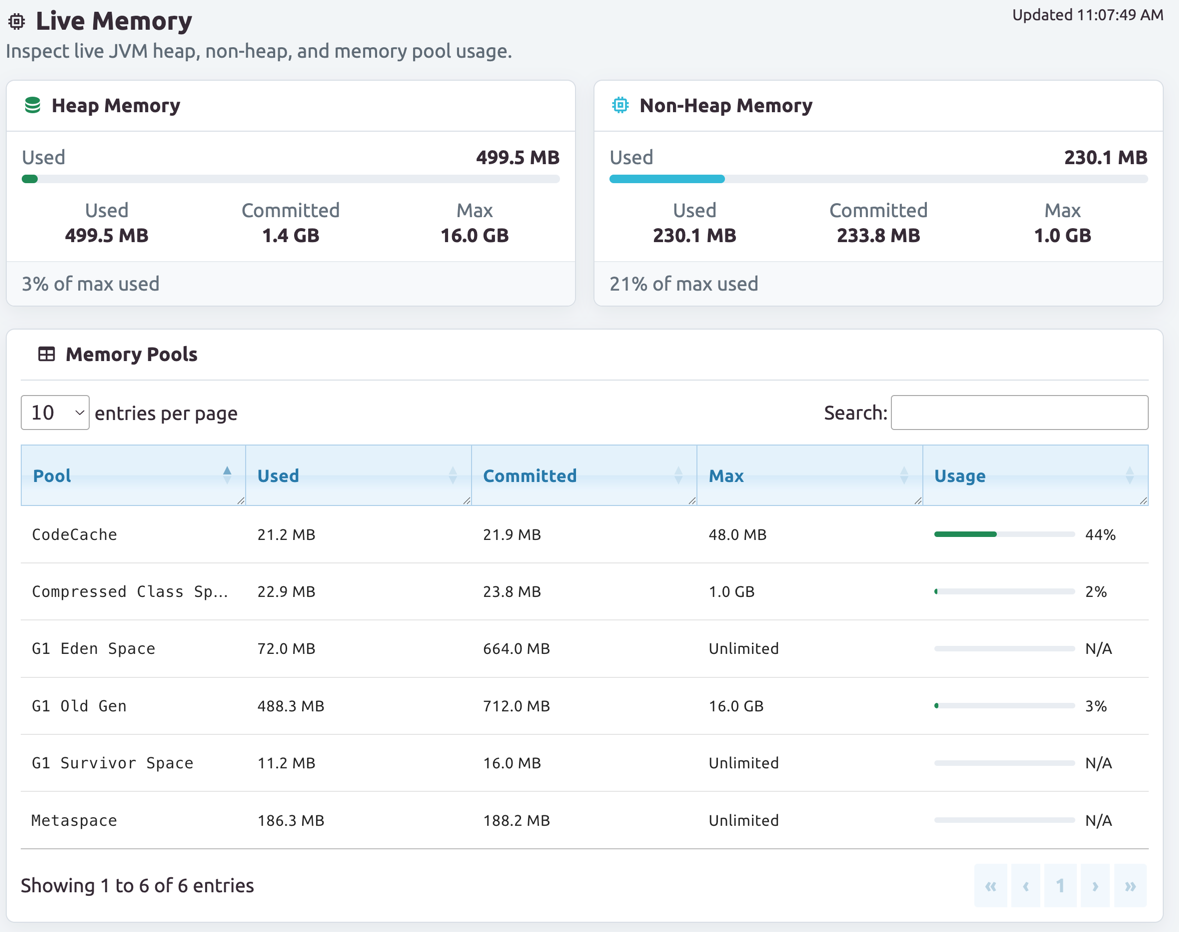
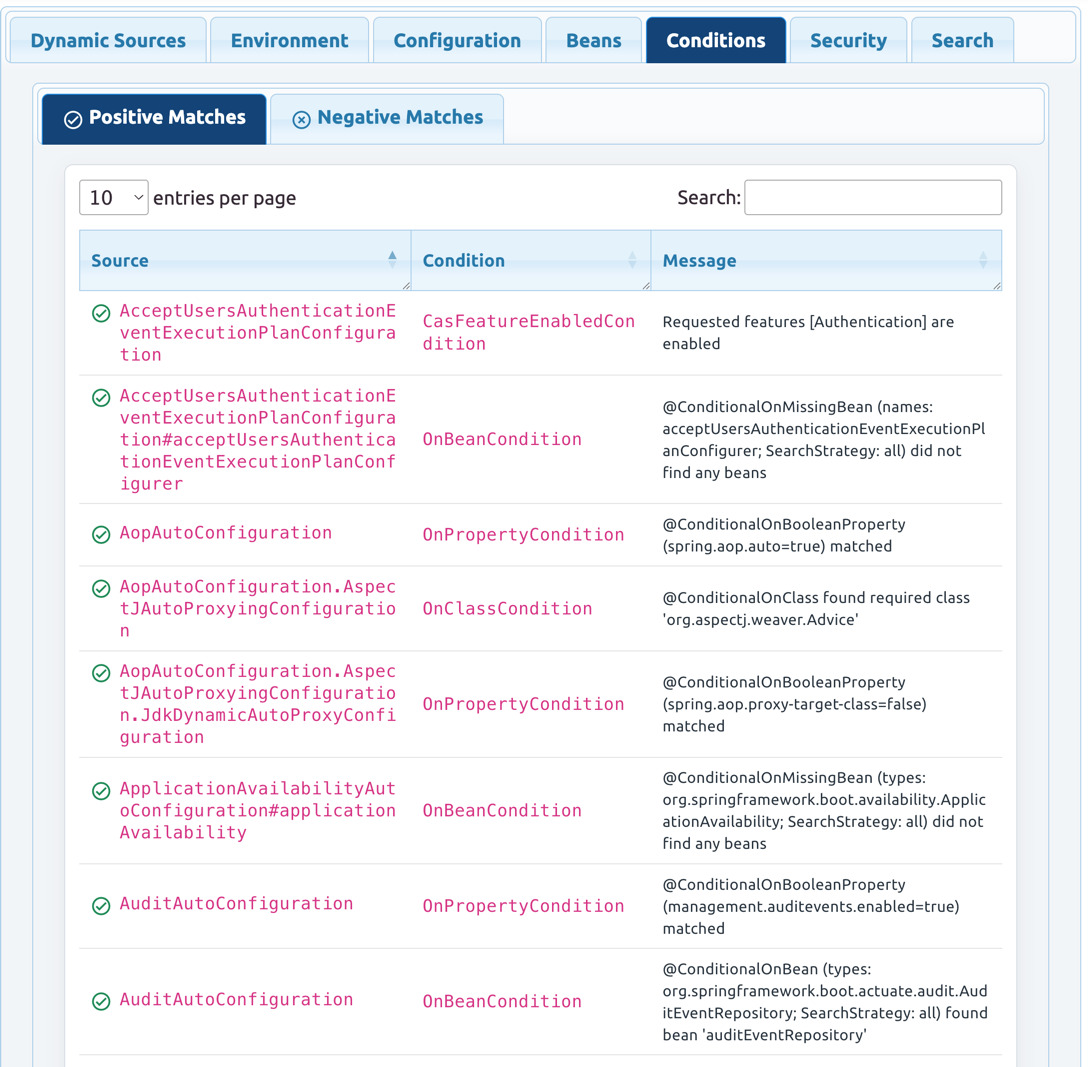
Inlined table buttons in Palantir Admin Dashboard are replaced with proper context menus triggered by right clicks. The configuration tab is also extended to display cached scripted resources with the ability to either remove or recompute the cache entry.
Furthermore, Heimdall authorization policies can now be created, edited and removed from the Palantir Admin Dashboard. There is also dedicated simulation support to experiment with authorization requests.
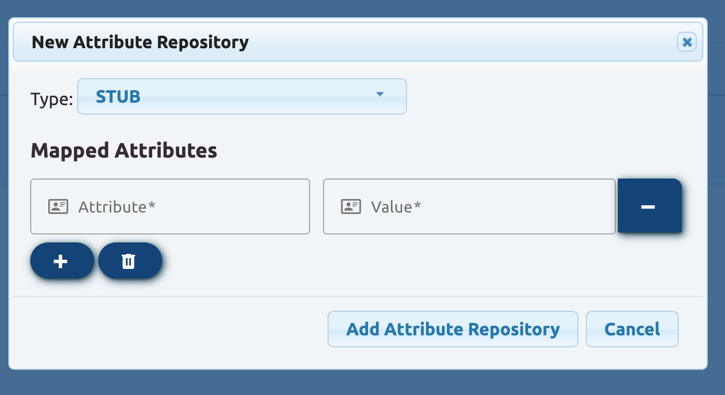
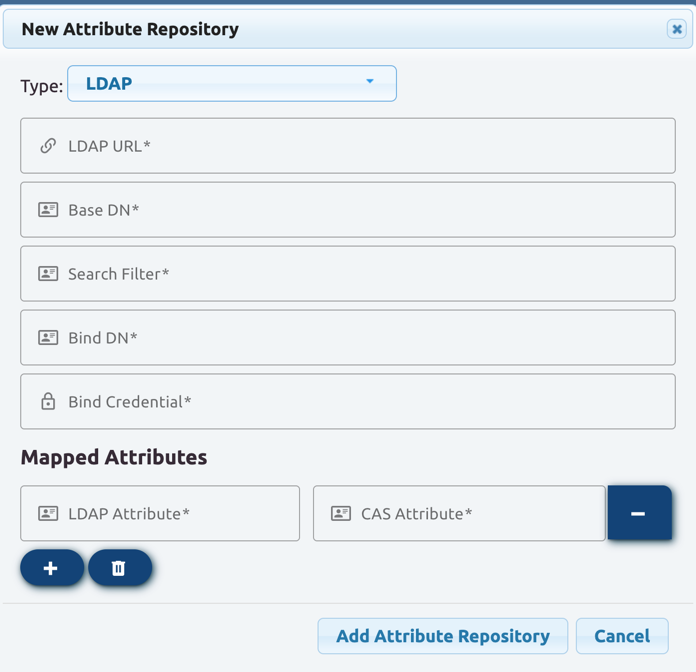
Configuration for almost all attribute repositories can also be viewed in better detail. The dashboard is also able to register new attribute repositories for LDAP, JDBC and Stub repositories.
Finally, fields that do support inline Groovy scripts are also allowed to better receive their value from a dedicated editor.
Palantir User vs. Admin Roles
The Palantir Admin Dashboard now supports basic user roles and permissions.
By default, all authenticated users are assigned a ROLE_USER role/authority. To access critical functionality as an admin,
you will need to resolve and release a role attribute to Palantir with a value of ADMIN or ROLE_ADMIN if you are
accessing Palantir via external CAS authentication, or your configuration needs to assign the authenticated user role
via spring.security.user.roles=ADMIN.
At this moment, all Palantir functionality is disabled and hidden for non-admin users, except for the ability to manage the list of registered applications.
Cluster Topology
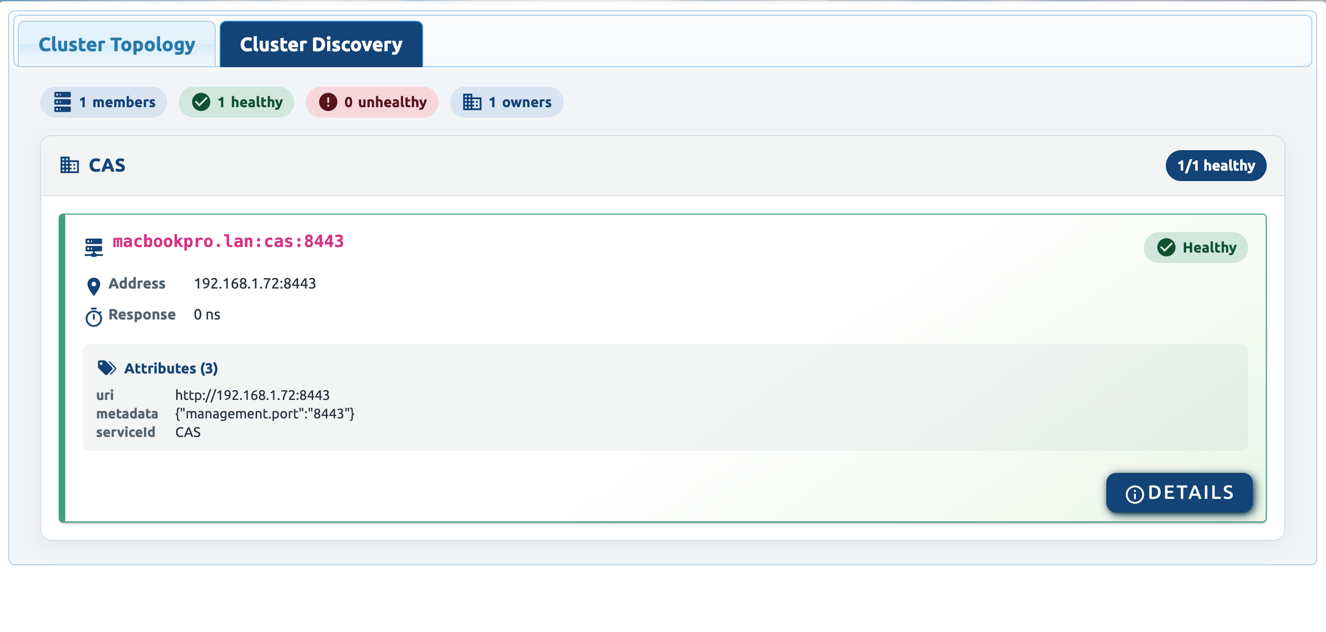
A new clusterTopology actuator endpoint is available to report on the current cluster topology
and the status of each node in the cluster, particularly relevant when CAS is running in high-availability mode.
Cluster topology support is available for the following features:
- MongoDb Ticket Registry
- Redis Ticket Registry
- Hazelcast Ticket Registry
- Apache Ignite Ticket Registry
- Apache Kafka Ticket Registry
- Apache Pulsar Ticket Registry
- Apache Geode Ticket Registry
- AMQP Ticket Registry
This capability is also supported and available for the Palantir Admin Dashboard.
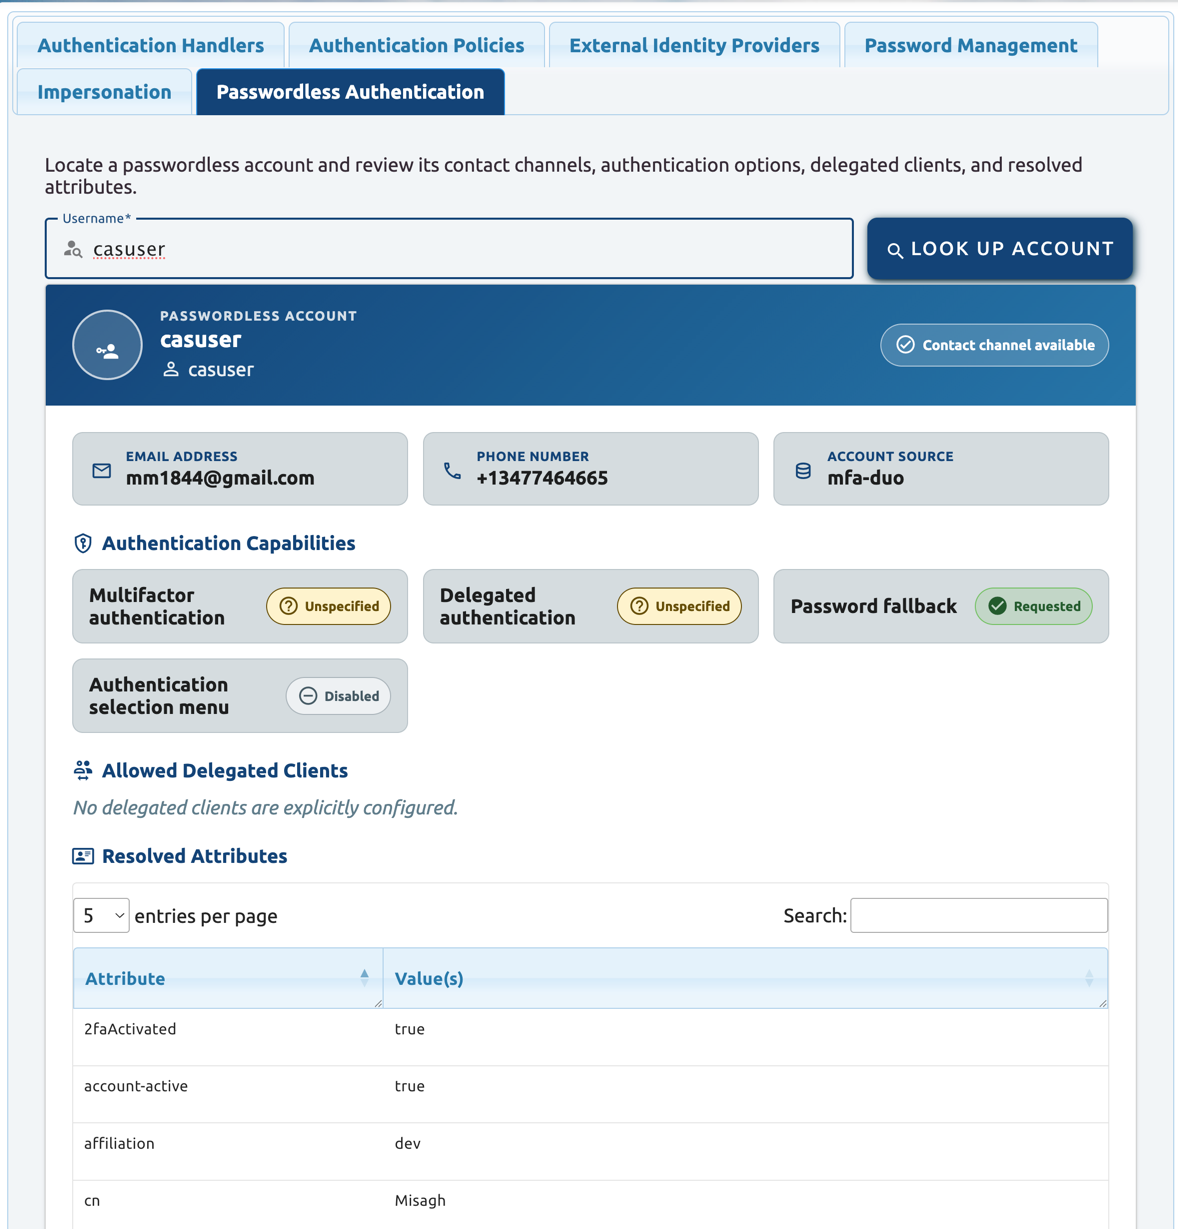
Passwordless Authentication
A dedicated actuator endpoint, passwordless, is available to allows one to query a username
and retrieve the associated passwordless account information.
This capability is also supported and available for the Palantir Admin Dashboard.
OpenID Connect Verifiable Credentials
OpenID Connect with Verifiable Credentials now supports the authorization code flow. There are also significant changes in place to support more formats with additional bug fixes and enhancements, and an improved test suite to verify credential issuance. There is also initial support for OpenID Connect with Verifiable Presentations (OpenID4VP).
OpenID Connect Federation
Work on OpenID Connect Federation is now roughly finalized. A number of test scenarios and minor edge cases are still being worked on and should be resolved in the next few releases.
Acceptable Usage Policy & Multitenancy
Acceptable Usage Policy (AUP) support has been extended to support multitenancy. A number of storage mechanisms are now available to support multitenancy, specifically MongoDb and more will be added in the future.
Other Stuff
Authentication
- When removing cookies, particularly during logout, the existing cookie value is no longer echoed back for remove operations.
Multifactor & Passkeys
- Multifactor authentication may also be activated using SAML2 metadata entity attributes.
OAuth & OpenID Connect
- Custom ID token claims can also be constructed using Apache Groovy.
CAS & Other Protocols
- CAS REST APIs now return a
403status code instead of a500type of error when unauthorized application requests are identified.
Attributes & Consent
- Releasing attributes via pattern matching accepts Groovy transformation rules.
- Attributes requested for Consent may now be localized using language bundles and a prefixed language key that is
screen.consent.attributes.attribute.[attribute-name].
Tickets & Sessions
- RediSearch functionality now supports Redis clustering.
- The maximum lifetime of a transient session ticket (i.e.
TST) is by default reduced from15minutes to5minutes. - LettuceMod is removed from CAS and its functionality is directly provided by Lettuce itself.
Build & Project
- A large number of dependencies and libraries have been updated to their latest versions.
- Groovy integration tests have now switched to use Groovy
5.1.x. - Redis integration tests have now switched to use Redis
8.10.x.
General
- A number of date-formatting operations have switched their base timezone from system default to
UTC.